Microservices best practices are the habits that keep many small services manageable, and a team does not need all of them on day one. Some prevent damage before the first service ships, and others only pay off once several services run together.
This guide sorts the best practices for microservices into three rungs and shows how to check that you follow each one in a custom software development project. The order is TekRevol’s judgment, and the sources support each practice but not the sequence.
What are the best practices for microservices?
The practices that keep microservices manageable are working rules for the design, data, communication, security, and operation of a system built from small independent services. They exist because many services bring problems that one codebase does not, such as network failures and scattered data. For rules that apply to any architecture style, see TekRevol’s guide to software architecture best practices.
The Azure Architecture Center describes most of the practices below, and this guide adds an order and a check for each one. The check and mistake columns in the tables are TekRevol’s reading, except where the text cites Microsoft. If you are new to the style, start with our guide to microservices architecture, which explains the parts and the trade-offs.
The TekRevol Practice Ladder: what to adopt first
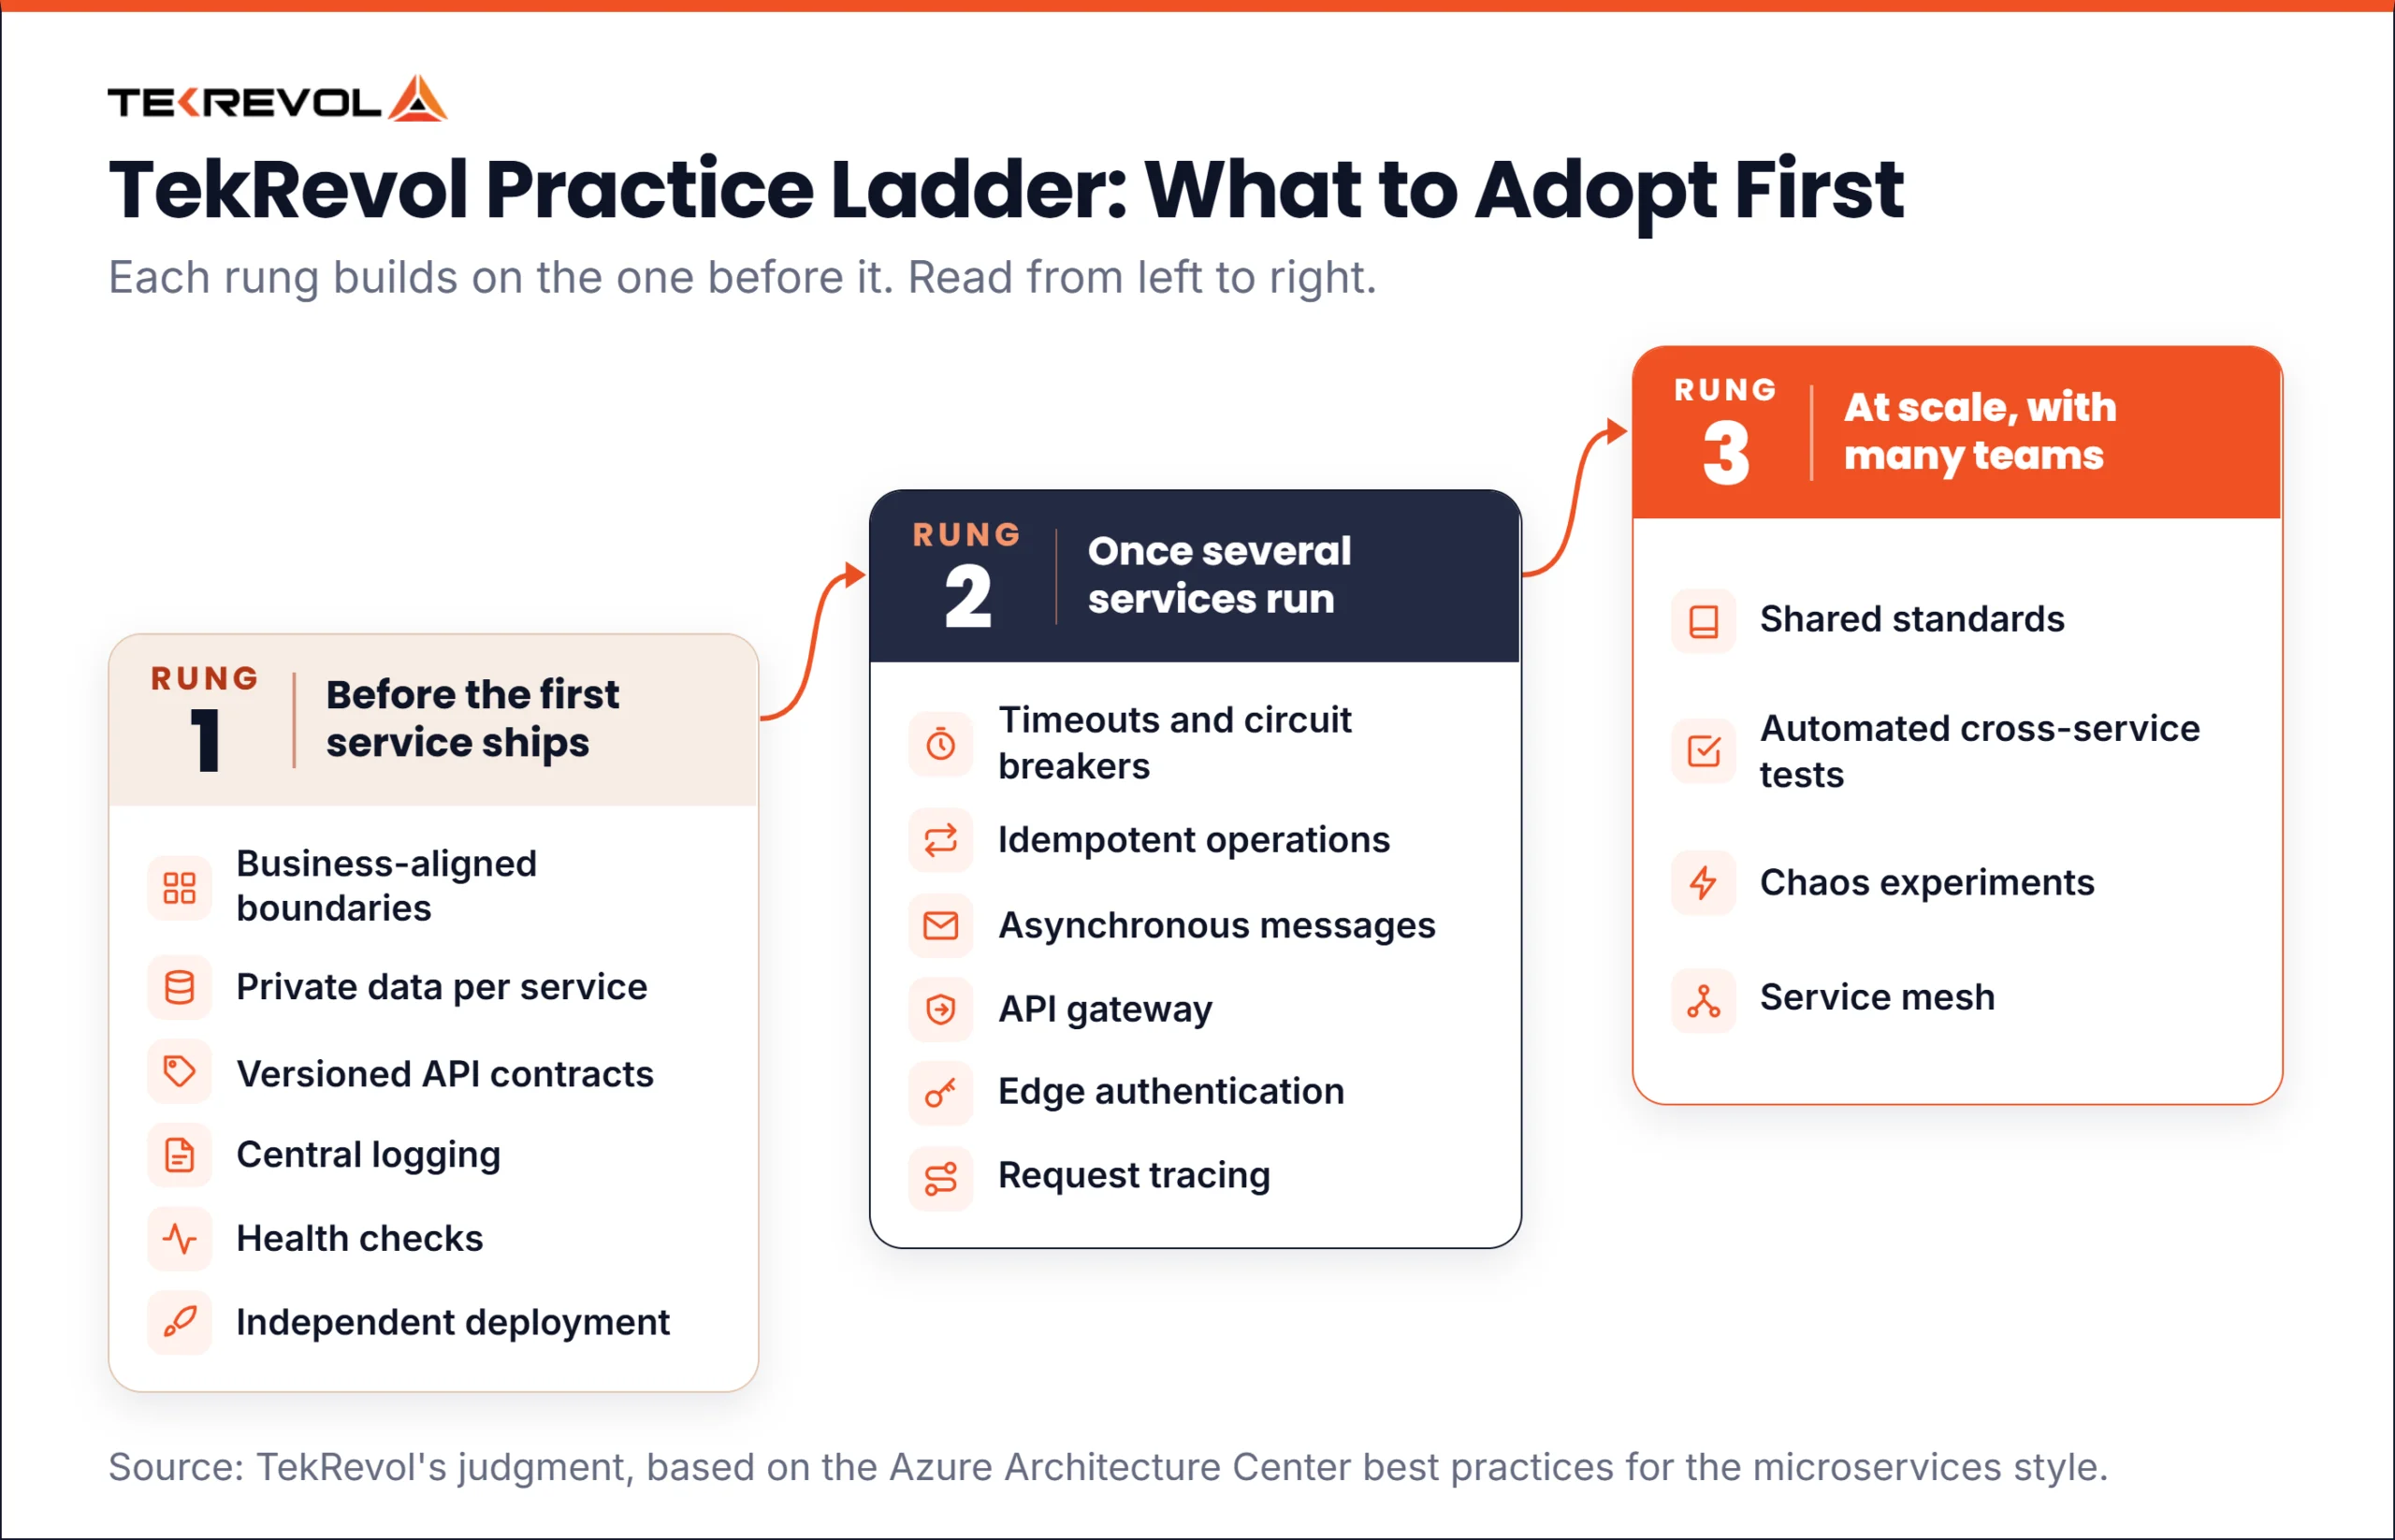
Adopt the practices in three rungs, starting with the ones every project needs. The TekRevol Practice Ladder is our judgment, and the diagram below shows the rungs. Each rung builds on the one before it.
| Rung | When you need it | Practices |
| Rung 1 | Before the first service ships | Business-aligned boundaries; one job per service; loose coupling, high cohesion; private data per service; versioned API contracts; central logs with correlation IDs; health checks; independent deployment |
| Rung 2 | Once several services run | Data copies where needed; timeouts on every call; retries with limits and circuit breakers; idempotent operations; asynchronous messages; API gateway for outside traffic; authenticate once at the edge; authorize near the data; distributed tracing |
| Rung 3 | At scale, with many teams | Secure service-to-service traffic; shared standards; chaos experiments; service mesh |
In TekRevol’s judgment, read the ladder as a default sequence. A small product may stay on rung 1 for a long time, and a system with regulated data may need a rung 3 practice early.
Microservices design best practices
The core design practice is to draw service boundaries around business capabilities and give each service one job. Microsoft’s guidance recommends modeling services around the business domain, and it describes building microservices without understanding that domain as an anti-pattern. Loose coupling and high cohesion follow from that: a change in one service rarely forces a change in another, and each service stays focused on one job.
| Practice | How to check you follow it | Common mistake |
| Business-aligned boundaries (rung 1) | Each service maps to a capability that a business person can name | Splitting before the domain is understood |
| One job per service (rung 1) | You can describe the service in one sentence, and most changes touch one service | A service that grows a second purpose and needs two teams to change |
| Loose coupling, high cohesion (rung 1) | A change in one service rarely forces a change in another | Services that must always be released together |
These rules also answer how to go about designing a microservice: start from the business capability, then decide its data and its API. Our guide to microservices design covers those decisions in more depth.
Data and API contract best practices
One service should own each piece of data, and every change to an API should be versioned. Private data means other services read it only through the owning service’s API, so a schema change stays inside one service. Microsoft’s guidance says data storage should be private to the service that owns the data.
Two habits follow from that rule: avoid shared schemas, and accept some duplicated data where it keeps services independent.
| Practice | How to check you follow it | Common mistake |
| Private data per service (rung 1) | No other service queries this service’s tables directly | Several services sharing one database schema |
| Versioned API contracts (rung 1) | Every API has a written contract and a version, and old versions keep working during a change | Changing a response shape and breaking callers |
| Data copies where needed (rung 2) | A service keeps a read-only copy of data it needs often and knows how it is refreshed | Banning all duplication, so every request waits on another service |
In TekRevol’s reading, versioning comes down to one habit: add to an API, and keep the old version running until every caller has moved.
Communication and resilience best practices
Set a timeout on every call between services first, then add retries, circuit breakers, idempotency and asynchronous messages. A slow service can drag down every service that waits on it, so Microsoft’s guidance recommends resiliency strategies that stop failures from cascading.
| Practice | How to check you follow it | Common mistake |
| Timeouts on every call (rung 2) | No call waits forever, and each timeout is set on purpose | Default timeouts that are far too long |
| Retries with limits and circuit breakers (rung 2) | Retries back off and stop, and a failing service is cut off | Retrying without limit, so a struggling service gets more load |
| Idempotent operations (rung 2) | Repeating a request leaves the same result | A retried payment request that charges twice |
| Asynchronous messages (rung 2) | Events carry work that needs no reply | Generic events that force consumers to interpret and filter them |
| API gateway for outside traffic (rung 2) | Clients reach services only through the gateway, and the gateway holds no business logic | Exposing services directly to clients |
Use messages where the caller does not need a reply, and keep long chains of synchronous calls short, because each extra call adds delay. Route outside traffic through an API gateway, because Microsoft’s guidance describes exposing services directly to clients as an anti-pattern.
Microservices security best practices
Authenticate users once at the gateway, and authorize each action inside the service that owns the data. Authentication proves who the caller is, and authorization decides what the caller may do, which is why microservices authorization best practices keep the decision close to the data. Microsoft’s guidance adds that traffic between services should be secured with mutual TLS and role-based access control, and that service meshes can help with cross-cutting concerns such as mTLS authentication and resiliency.
| Practice | How to check you follow it | Common mistake |
| Authenticate once at the edge (rung 2) | Token validation happens at the gateway | Token validation code copied into every service |
| Authorize near the data (rung 2) | Each service decides what a caller may do with its own data | Trusting every request that passes the gateway |
| Secure service-to-service traffic (rung 3) | Services prove their identity to each other, and traffic is encrypted | Treating the internal network as trusted |
Microservices monitoring and logging best practices
Microservices monitoring best practices start with two habits: collect every service’s logs in one place and tag each request with a correlation ID, so one user action can be followed across services. Microsoft’s guidance names centralized logging and distributed tracing through OpenTelemetry, and it notes that correlating logs for one operation is a challenge. Health checks are the cheapest start, because each service exposes a status endpoint and the platform stops sending traffic to an unhealthy instance.
| Practice | How to check you follow it | Common mistake |
| Central logs with correlation IDs (rung 1) | Given one request ID, you can see its path through every service | Logs left on each server, so tracing means logging in to many machines |
| Health checks (rung 1) | Every service has a status endpoint that monitoring reads | Checking only that the process runs |
| Distributed tracing (rung 2) | A slow request shows which service caused the delay | Metrics per service with no view across services |
Deploying and managing microservices
Deploy each service on its own through an automated pipeline, and keep configuration outside the code. Independent deployment is the point of the style, so one team’s release should never wait for another’s. Microsoft’s guidance recommends automating testing and deployment with CI/CD, and it describes configuration values kept inside services as an anti-pattern.
To manage microservices at scale, teams use an orchestration platform to place services on machines and restart them when they fail. Best practices for microservices development end with testing: Microsoft recommends chaos engineering to check that failures stay contained, and in TekRevol’s judgment that belongs on rung 3, after the basics work.
Microservice standards: what to share and what to leave free
Share rules that apply across services, such as logging format and deployment steps, and leave internal design to each team. Microsoft’s guidance warns that too many languages and frameworks create a governance problem, and it recommends project-wide standards for cross-cutting concerns such as logging.
Without shared standards, each team builds its own logging and its own checks, and the cost shows up when someone has to trace a failure across different formats. In TekRevol’s judgment, standardize the cross-cutting rules first and allow a second language only when a service needs it.
Microservices anti-patterns to avoid
Microsoft’s guidance describes anti-patterns that undo the practices above. TekRevol selected six of them for the table.
| Anti-pattern | Why it hurts | Fix |
| Building before the domain is understood | Boundaries land in the wrong place and are costly to move | Model the business domain first |
| Sharing common libraries or dependencies | A change in one service breaks others | Share contracts between services |
| Exposing services directly to clients | Clients depend on internal details of each service | Route outside traffic through the gateway |
| Configuration values kept inside services | Services become tied to specific environments, which makes deployments harder | Keep configuration outside the code |
| Token validation inside every service | The same security code is repeated and can drift apart | Validate tokens at the gateway |
| Generic events | Consumers must interpret and filter messages | Name each event for what happened and carry the data consumers need |
When the full set of practices is overkill
Knowing when to use microservices comes before knowing how to run them: a small product with one team gains little from the full ladder. Martin Fowler’s Microservice Trade-Offs article names three costs: distribution, eventual consistency, and operational complexity, and says to weigh them in your own context.
If you are unsure whether you need services at all, the TekRevol Service Split Check asks five questions before you commit. In TekRevol’s judgment, a team of one or two can stay on rung 1 inside a modular monolith and revisit the ladder when releases start blocking each other. TekRevol’s comparison of monolithic vs microservices covers that choice in more detail.
Putting these practices into a real project?
TekRevol, a software development company, sets up cloud environments and CI/CD pipelines at launch in its custom software development process, and each two-week sprint ends with tested software.
Bring your current services and delivery pipeline to the table, and we will help you place them on the ladder and choose the next practice to adopt. Adopt the next rung when the last one is working. Start with a Free Consultation.